This is a version of Fake Branded Online Store Scam.
Fake SHEIN Store Selling Designer Bags and Phones
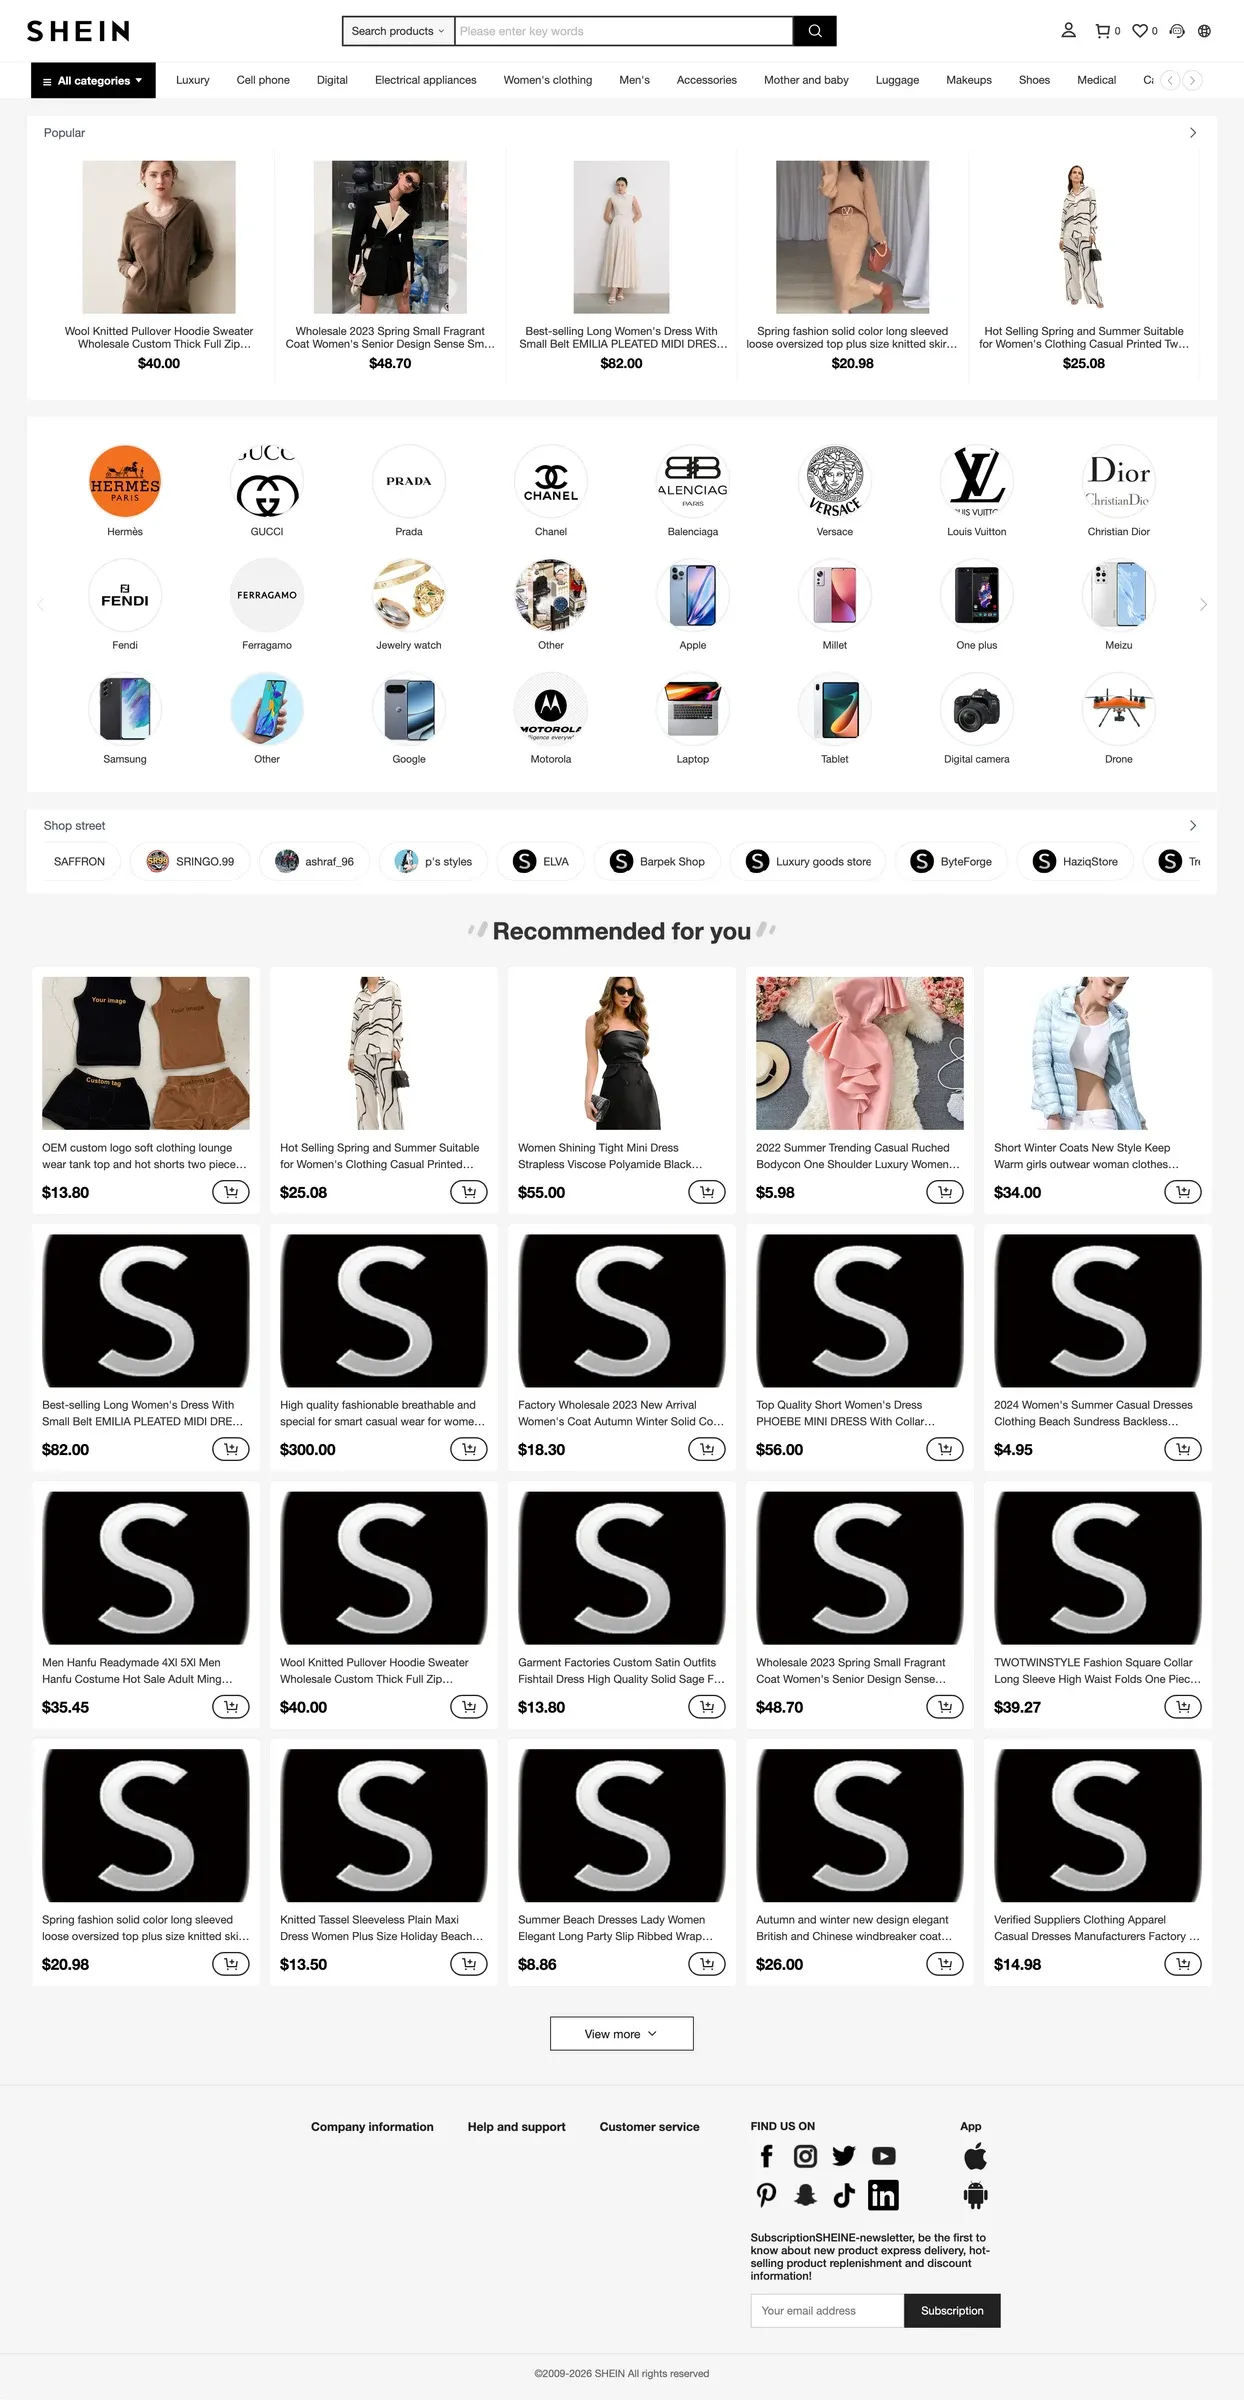
A shop carrying the SHEIN wordmark and a footer reading "©2009-2026 SHEIN All rights reserved", at shein[.]brinqu[.]com. The brand name sits to the left of the real address: the site is brinqu[.]com, and "shein" is a label in front of it. The catalogue does not match the real retailer. Alongside women's clothing it offers Luxury, Cell phone, Digital, Electrical appliances, Medical, Car Products and Musical instrument, with brand tiles for Hermès, Gucci, Prada, Chanel, Balenciaga, Versace, Louis Vuitton, Christian Dior, Fendi and Ferragamo, then Apple, Samsung, Google, Motorola, Xiaomi, OnePlus, Meizu, laptops, tablets, cameras and drones. A "Shop street" row lists third-party sellers the real retailer does not have. Product titles are scraped wholesale copy, mentioning "OEMservice", "Custom Labels" and "Verified Suppliers ... Manufacturers Factory In China". Roughly half the product tiles show a placeholder letter where the photo failed to load, and the same listing appears more than once at the same price. The site offers accounts, a basket, orders and a customer service chat.
What’s different in this version
These traits set this message apart from the usual pattern.
-
The brand taken is SHEIN, a clothing retailer, while the shop sells designer handbags, phones, drones, car products and medical items.
-
The address puts the brand name to the left of the real one, so it reads correctly at a glance: the site is brinqu[.]com, not shein.com.
-
Nothing about the page's appearance gives it away. It is a competent copy, and the only reliable tell available to a reader is the web address itself.
-
Every automated check on it came back clean, including the certificate, Google Safe Browsing and page-content checks. The address was about 21 days old when reported.
How this scam works
- 1
Step 1: A shop appears at an address that carries a familiar retailer's name without being that retailer's website. The name is often placed to the left of the real address, so it reads correctly at a glance.
- 2
Step 2: The page copies the retailer's wordmark, colours and footer closely enough to pass a glance, including a copyright line in the real company's name.
- 3
Step 3: The goods on sale do not match the retailer: a clothing brand's shop offering designer handbags, phones, drones or car parts, with product text scraped from wholesale listings.
- 4
Step 4: The site behaves like a normal shop. It offers accounts, a basket, orders and a customer service chat, which is what makes a shopper willing to type things into it.
- 5
Step 5: Anything entered goes to whoever runs the site rather than to the retailer, because the retailer has nothing to do with it.
✓ Do this
- Read the web address from the right. The real site is the last part before the first single slash, and a brand name in front of it is just a word somebody chose.
- Go to the shop the way you normally would, through its own app or by typing its address yourself, and see whether the same offer exists there.
- If you have already paid, tell your bank or card provider straight away and ask about a chargeback.
- If you reused a password on the fake shop, change it everywhere else you use it, from a device you trust.
✗ Avoid this
- Do not judge a shop by whether it looks right, or by a safety checker finding nothing wrong. A copy can be good enough to pass both.
- Do not assume a padlock or 'https' means a shop is genuine. It only means the connection is private, not that the shop is.
- Do not enter a card, an address or a password on a shop you reached from a link, before you have checked the address.
- Do not trust a brand's logo, a copyright line, or a long list of well-known names on the page. All of those are copied in a few minutes.